Arbek Teknoloji
  1. Arbek
  2. Our Services
  3. Corporate VPN / SSL VPN Solutions

Corporate VPN / SSL VPN Solutions

End-to-end encrypted, redundant and continuously monitored corporate VPN backbone connecting your branches.

Corporate VPN / SSL VPN Solutions

The real test of an inter-branch VPN is not the day it is installed but the day a line goes down; that is why we deliver an encrypted backbone built on modern cryptography, together with dual-WAN redundancy, central key management and 24/7 tunnel health monitoring from our center in Ankara. Adding a branch is not a task reinvented every time; it is a standard procedure with the address plan and configuration template ready. We do not let POS, camera and office traffic mix inside the same tunnel; segmentation has been part of this architecture from the start, the same architecture we operate in production across fuel station networks.

Site-to-site and client VPN architectures with redundant links and central monitoring for uninterrupted branch connectivity.
01.

How the backbone works

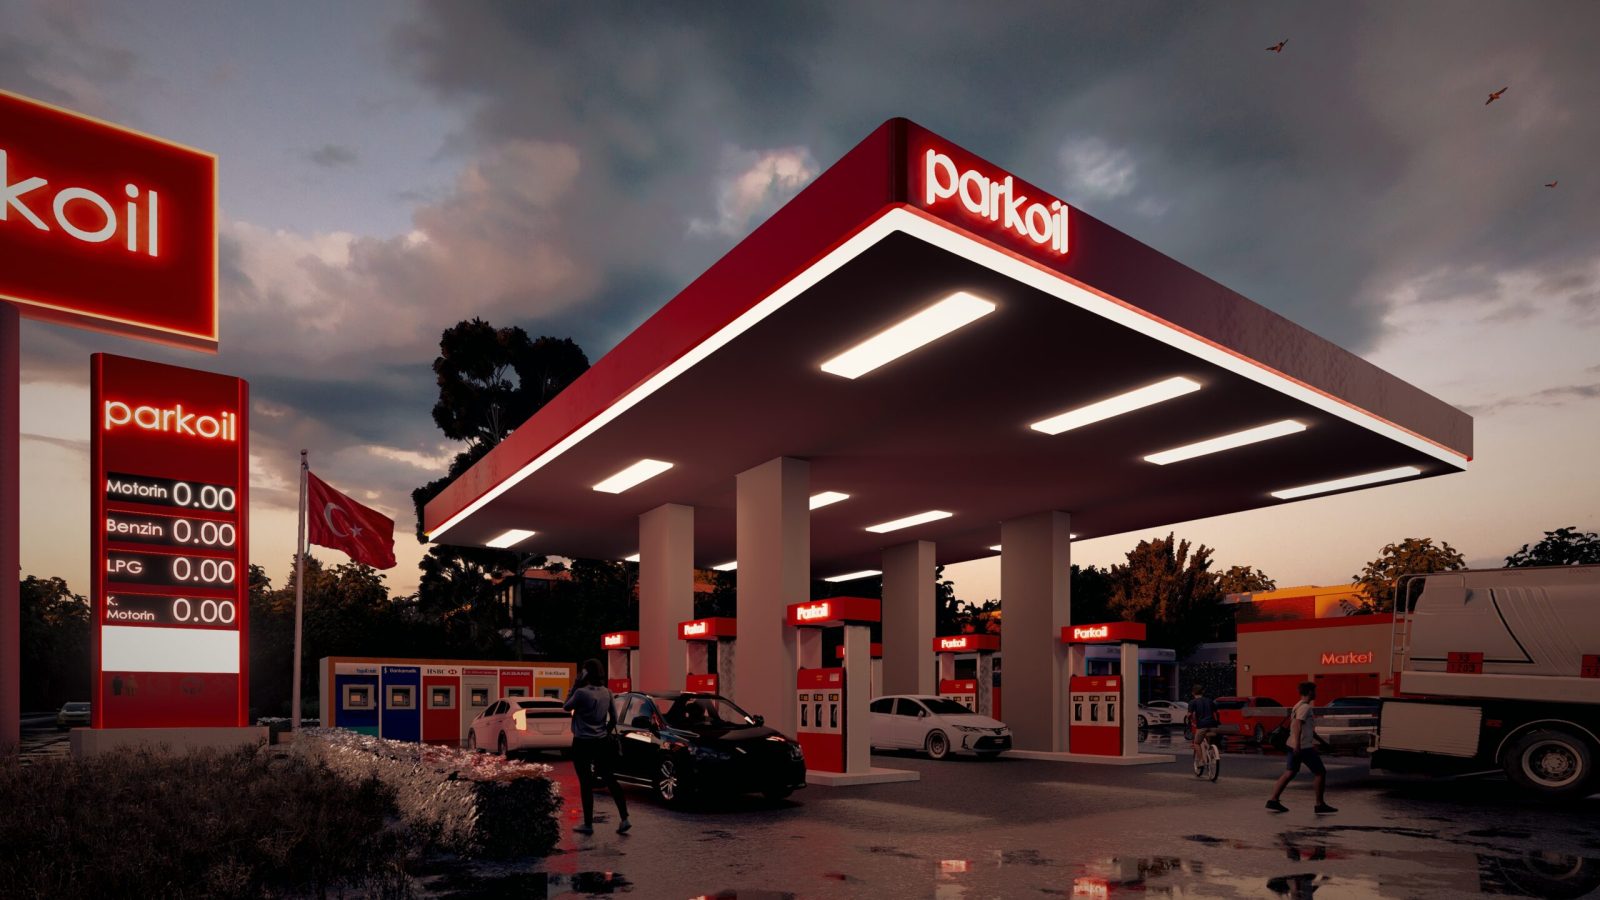
Data is encrypted at the station and travels through a private tunnel to the distribution company's headquarters; if a line drops, the backup takes over. ArbekWatch monitors every tunnel 24/7.

02.

What this service covers

01
End-to-end encrypted VPN backbone

Inter-branch traffic is carried in end-to-end encrypted tunnels using modern cryptography; a tunnel keeps the session alive even when an endpoint's IP address changes.

02
Central key management

Branch and user keys are generated, distributed and revoked centrally; access for departed staff or a removed device is closed with a single operation.

03
Redundant lines with dual WAN

Each branch is provisioned with two separate internet uplinks; when the primary line fails, traffic moves to the backup automatically and is switched back once the line recovers.

04
24/7 tunnel health monitoring

Latency, packet loss and tunnel drops are continuously tracked at our monitoring center in Ankara; the alarm reaches our team before a fault report arrives from the branch.

05
Branch onboarding standard

A new site is added with a ready address plan, configuration template and commissioning checklist; every branch goes live through the same procedure, not by improvisation.

06
Remote access over SSL VPN

Staff connecting from home or the field pass authentication and reach only the internal resources they are authorized for; defined services are exposed, not the whole network.

07
Network segmentation

POS, camera and office traffic travel in isolated segments; a vulnerability in a camera cannot reach the POS devices, and an issue on the office network cannot reach the cameras.

08
On-site installation, continuous operation

Branch hardware is installed on site by our field team across Turkey; after commissioning, we take over the operation and monitoring of the network.

03.

How we proceed

  1. 1 Discovery and current-state analysis Branch count, line types, existing network equipment and application traffic are documented; POS, camera and office flows are mapped.
  2. 2 Design and addressing plan The topology (hub, redundancy, segments) and the per-branch IP address plan are defined; the branch onboarding template is written at this stage.
  3. 3 Pilot deployment A pilot goes live with the head office and a small set of selected branches; failover scenarios are tested by physically pulling the line.
  4. 4 Rollout Remaining branches are commissioned in sequence using the standard procedure; no branch counts as delivered until its commissioning checklist is complete.
  5. 5 Operation and 24/7 monitoring Tunnel health is continuously tracked from our monitoring center; fault, capacity and change management run as part of the operation.
04.

Frequently Asked

We already have a VPN in place; will migration cause an outage?

The migration is planned in stages: new tunnels are built alongside the existing setup, traffic is moved branch by branch, and the old infrastructure is switched off last. Whether a maintenance window is needed becomes clear during discovery, based on each branch's line and hardware situation.

What happens when an internet line goes down?

At a branch with dual WAN, traffic switches to the backup line automatically; the drop raises an alarm at our monitoring center and line health is tracked. For single-line branches, redundancy options are proposed during discovery.

How is remote staff access over SSL VPN restricted?

Access is defined per user and limited to the internal resources actually needed; the authentication method, including integration with your existing directory infrastructure, is determined by the scope.

Why separate POS and camera traffic?

On a single flat network, a vulnerability in the cameras can reach the POS devices; segmentation cuts off this lateral movement at the network level. Which segments to create is decided during discovery based on the device inventory at the branches.

Get a quote for Corporate VPN / SSL VPN Solutions

Reach out for a survey and offer; we reply within 24 hours.

Get a Quote Ara